2 November 2026 Governed NoOps, part 1: building software got cheap, running it must too AI made writing software cheap but not running it, and the threat moved the other way. Part 1 of the Governed NoOps series sets out the idea and the set-up behind it.
2 November 2026 Governed NoOps, part 2: the paved road Part 2 of Governed NoOps: one shared platform carries the hosting, security and patching, every change travels dev to staging to production, and the patching policy's defaults come with their reasons.
2 November 2026 Governed NoOps, part 3: compliance that can't go stale Part 3 of Governed NoOps: write each fact once, next to the code it describes, generate the evidence from it, and let a test fail when the two disagree.
2 November 2026 Governed NoOps, part 4: manage the agent like a team member Part 4 of Governed NoOps: running an agent well takes the same skills as leading a team. Inform, Consult, Escalate, with a second, independent actor on anything that could change the rules.
2 November 2026 Governed NoOps: AI-built software is now cheap; to remain secure it must be just as cheap to maintain and operate AI has made writing software cheap but not running it. Governed NoOps points the same tools at upkeep and compliance evidence: a platform that carries the weight, compliance generated from code, and agents managed like a team, with two actors on the red lines.
2026 · ContributionState of AI in Security & Development 2026 Survey report on the risk of AI-generated code. Quoted on the lack of clarity over who is accountable when GenAI code causes an incident. Contribution at Aikido Security, on Aikido.
7 December 2025 Schrödinger's AI: Brilliant or Stupid Until Inspected Current AI is both brilliant and stupid until you look carefully at what it produced: you find out which only by checking its work, with the knowledge to tell a useful result from a convincing hallucination.
10 November 2021 · TalkAn Evolution in the Cybersecurity Landscape A podcast discussion with Matthew Chung and Wesley Williams on how cyber attacks have grown and how defences have adapted to new threats (about 24 minutes). Talk at Exchanges at Goldman Sachs, on Apple Podcasts.
16 October 2021 · ContributionOverrated/Underrated with Andy Boura An interview, with a recorded discussion, giving views on whether a series of security topics are overrated or underrated. Contribution at Dr Daniel Schatz, LinkedIn, on LinkedIn.
11 May 2021 Effective Business Writing Practical advice on writing for busy readers: think about the audience, keep it brief, structure it with McCarthy's 4MAT, put the bottom line up front, and make a few strong points rather than many weaker ones.
22 November 2020 The Priority Matrix A two-step way to triage work: place each task on an importance and urgency matrix, using MoSCoW labels, then apply the tactics that suit its quadrant, so that more time goes on work that is important but not urgent.
14 November 2020 Effective Delegation through Active Calibration A method for deliberately calibrating decision-making authority in a new role or with a new team member: sort decisions into those to inform on, consult on and escalate, then shrink the grey consult area over time.
2 November 2020 Compositional Reporting | Meaningful Updates in a Complex Environment Proposes security reporting built from short, current executive summaries that each domain expert keeps for each product, combined into overviews for different audiences, with notes on writing good executive summaries.
9 October 2019 · TalkEuropean Banking Forum: Technology, Security and Risk 2019 Speaker at the London forum on balancing innovation with security in financial services, taking part in a question-and-answer session on emerging trends, risks and opportunities. Talk, on Arena International.
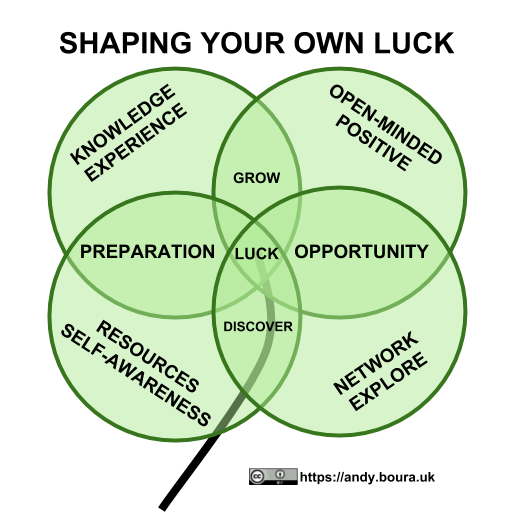
8 February 2019 Shaping your own luck A short personal piece arguing that much of luck is made: being open-minded and exploring finds opportunities, and knowledge, experience and preparation let you make the most of them.
17 July 2018 · ContributionManage Security as a Shared Responsibility A contribution to a Mighty Guides e-book of security leaders’ advice, arguing that security works best as a responsibility shared across the organisation rather than left to the security team. Contribution, on Mighty Guides.
2 February 2017 · TalkSecurity by Nature not Nurture A keynote linking Agile, cloud and third-party risk. Talk at CISO Inspired, Inspired Business Media, on YouTube.
2017 · TalkDoes Big Data Have to Mean Big Risks? Breach costs rising with data volume, the main sources of risk (user error, system glitches and attacks), and controls such as access management, automation and data hygiene. Talk at Big Data Week London 2017, on SlideShare.
30 December 2016 · ContributionShould C-Level Bonuses Be Linked to Cybersecurity Success? A feature by Sooraj Shah on whether executive pay should depend on cyber security, after MPs proposed it. Quoted on why the intent is sound but the difficulty lies in putting it into practice, and why box-ticking is not enough. Contribution, on Infosecurity Magazine.
24 May 2016 · TalkSetting Ourselves up to Fail - The Need for Security Awareness Marketing and Consistency Through the use of marketing techniques organisations can get the security awareness message over more effectively. Combined with "fallibility aware" systems design, itself part of developer and architect security awareness, we can protect systems much better than we currently do. Though if we don't follow our own rules consistently we are setting ourselves up to fail... Talk at Whitehall Media, on YouTube.
7 March 2016 Gone Phishing: a genuine text that looked like a scam, and the lessons for any organisation A convincing text message about renewing an official document linked to a third-party survey site. The government's own phishing team said it was a scam; it turned out to be genuine. The warning signs, what went wrong, and lessons for any organisation moving services online.
8 December 2015 Advocating the rise of the Security Awareness Marketing function Argues that security awareness should be run as marketing, with marketing's creativity, metrics, audience segmentation and specialists delivering core messages that security experts identify.
20 October 2015 IoT Security: Beware Ghost Ships and Trojan Horses Argues that the bigger IoT security risk is devices their makers abandon, left unpatched on home networks, and gives advice for device designers and for consumers.
21 May 2015 Don't focus on the weakest link; correctly combine likelihoods Explains, with a worked example, why security is not only as good as its weakest link: the likelihoods of separate risks combine, so several modest risks together can outweigh the weakest one.
24 April 2015 7 Types of Breach Costs; Things to Consider When Estimating Impact Drawing on large breaches such as Home Depot, Target and Anthem, sets out seven types of cost to consider when estimating the impact of a data breach, and argues that investing in security now makes financial as well as moral sense.
19 March 2015 Biometrics: The Hazards, and Mitigations, for Effective Use Weighs the strengths and weaknesses of biometric authentication, prompted by Windows 10's support for it, and argues that biometrics should unlock a key held in tamper-resistant hardware rather than act as the credential themselves.
31 January 2015 FAQ for RC ESC (electronic speed controller) calibration, programming and use with Arduino for multicopters A hobbyist's FAQ on driving RC electronic speed controllers from an Arduino for multicopters: calibration and programming with the Servo library, pulse widths and timing, motor direction, and matching the ESC, motor, propeller and battery.
2015 · ContributionHow can you predict the impact of the inevitable data breach on your organisation? Coverage of a panel at Computing’s Enterprise Security and Risk Management Summit on valuing information assets to predict the impact of a breach. Quoted on why "made-up numbers" are still worth estimating. Contribution, on Computing.
28 July 2014 · TalkEffective Security Architecture as a Foundation for Risk Reduction For senior managers: technical debt, security architecture, and examples of designing security in from the outset (16 minutes). Talk at Whitehall Media Enterprise Security and Risk Management Conference 2014, on YouTube.
 By Andy Boura